Seven years of breaking things professionally.
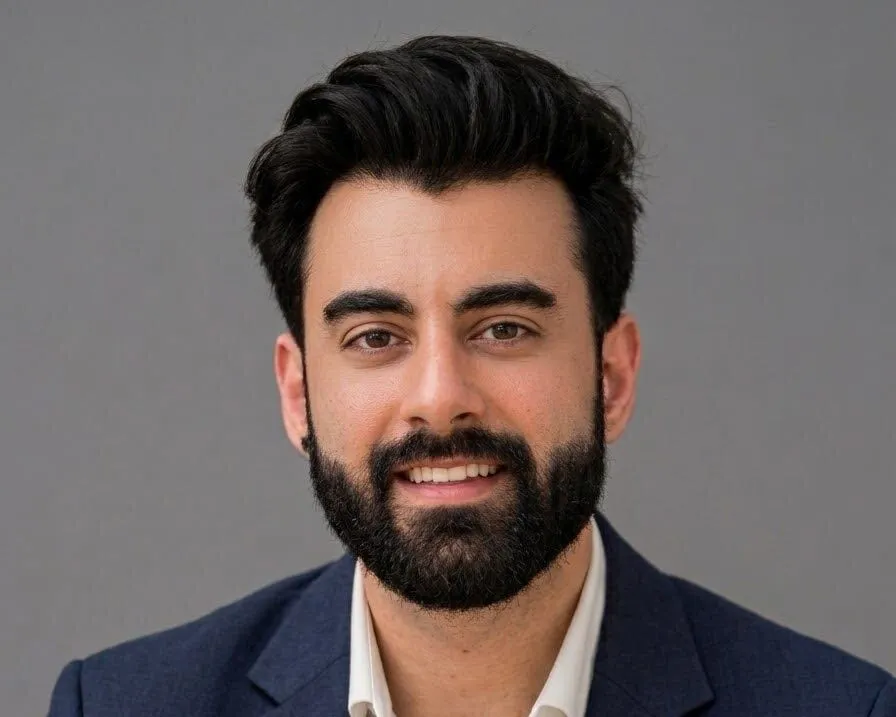
I'm Hotanya, a Senior Application Security Engineer at Plexure. I started in penetration testing, testing web, mobile, API, network and cloud for clients across New Zealand, and now lead application security inside a SaaS platform: secure design, vulnerability management and DevSecOps.
NowLeading application security at a SaaS platform.
Senior Application Security Engineer · Plexure
I run application security for the platform. That means owning the vulnerability management lifecycle from triage to validated fix, so findings close instead of ageing, and pentesting the web apps and APIs in-house, turning what I find into secure design patterns engineering actually adopts. I chose and wired SAST, DAST and SCA into CI/CD, with threat models that say why each check exists, and I support incident response with root-cause analysis so the same class of bug does not come back.
BeforePentesting and consulting, 2018 to 2026.
Penetration Testing and Security Consulting
I started at Insomnia Security in 2018 and moved onto the testing team the following year, testing APIs, web and mobile applications and internal and external networks. I stayed on through the CyberCX merger, where I led a team of junior consultants, helped start the NZ Associate Program and gave the keynote at the NZ Cyber Security Challenge in 2022. After that, a year embedding security into projects at Kiwibank, then lead consultant at Bastion Security, scoping and delivering tests and helping with pre-sales.
full history on linkedin →DisclosuresVulnerabilities I've found and reported, in open-source projects and vendor infrastructure.
| ID | Project | Issue | Status |
|---|---|---|---|
| CVE-2026-111442 | Backdrop CMS | Stored XSS via SVG Uploads | fixed · 1.35.2 / 1.34.6acknowledged ↗ |
| GHSA-8r9v-m73r-rmxf | Akinai | Server Code Execution via Crafted Theme | fixed · 0.0.2CVE pending |
| GHSA-46g5-g2v6-rcvh | Akinai | Privilege Escalation via Self-Editable Roles | fixed · 0.0.2CVE pending |
| CVE-2024-52286 | Stirling-PDF | Self-XSS in the Merge Feature | fixed · PR #2189 |
| — | Palo Alto Networks | Firewall Configs Exposed in Public S3 Buckets | fixed · Sep 2025acknowledged ↗ |
| — | es-hangul | Command Injection in a GitHub Actions Workflow | reported with fix PR |
| — | vitejs/vite | Admin-Scoped Algolia API Key Exposed | reported · resolved |
TalksConference and community presentations.
Thinking Like an Attacker: Quick Wins for Securing Your Application
OWASP AppSec Days India
Skills
Offensive Testing Web Applications, APIs, iOS and Android, Internal and External Networks and Active Directory.
Cloud AWS and Azure Security Reviews.
AppSec Programme Vulnerability Management, Secure SDLC and Threat Modelling.
DevSecOps SAST, DAST and SCA in CI/CD Pipelines, Infrastructure as Code with Ansible, Compliance as Code and DevSecOps Maturity Assessments.
Code Source Code Review, Python, Bash, PHP, C#.
AI Prompt Injection, LLM Penetration Testing and 'Secure' Vibe Coding.
CertificationsHeld, plus the two I'm working towards.
 in progress
 in progress
Want to work together?
Security reviews, speaking, or research collaborations.